Unable to find what you're searching for?
We're here to help you find itSecure systems by handling malware, email, and web application incidents using EC-Council’s ECIH methodology; train with officially credentialed instructors through hands-on labs and real-world scenarios to earn the ECIH 212-89 certification.


500K+ certified professionals
Explore Incident Handling and Forensics certification and training courses — delivered live by certified instructors.
Incident Handling and Forensics is a cybersecurity discipline focused on detecting, investigating, containing, and recovering from security breaches, published by EC-Council as part of its core digital forensics and incident response (DFIR) certification framework. It provides a structured methodology for identifying intrusions, preserving evidence, and supporting legal prosecution, forming a critical component of the organization’s broader threat intelligence and cyber resilience strategy. The technology encompasses Computer Hacking Forensic Investigator (CHFI), which covers forensic investigation across systems, networks, and digital media; Mobile Forensics, used to extract and analyze data from smartphones and tablets; Malware Analysis, for dissecting malicious software; Memory Forensics, to inspect volatile system memory; and specialized modules in Cloud Forensics, IoT Forensics, and Dark Web Forensics that extend investigative capabilities into modern attack surfaces. This technology is for cybersecurity analysts, digital forensics investigators, incident responders, and law enforcement personnel who must identify breach origins, preserve admissible evidence, and support organizational recovery with technical precision and procedural integrity.
Network Protocols
Understand TCP/IP, DNS, HTTP and common network services
Operating Systems
Navigate Windows and Linux file systems and core services
Command Line
Use CLI tools like PowerShell, Bash, tcpdump and Wireshark
Security Monitoring
Analyze logs, alerts and network traffic for anomalies
Incident Response
Apply IR processes such as detection, containment and eradication
Digital Evidence
Handle volatile data and disk artifacts following forensic order
The building blocks every Incident Handling and Forensics solution is made of
See what your official Incident Handling and Forensics certification looks like. Download a sample — then let our advisors map the fastest path to earning the real one.
 SY0-701Security+
CS0-004CySA+
GCIHGIAC Certified Incident Handler
GCFEGIAC Certified Forensic Examiner
GCFAGIAC Certified Forensic Analyst
CHFIComputer Hacking Forensic Investigator
Official credential badges — shareable on LinkedIn
Four formats. One quality standard. Every option comes with the same expert instructors, official courseware, and money-back guarantee.
Every factor that determines whether you actually pass your Incident Handling and Forensics exam — rated across every training format available.
| Criteria | Koenig | ALP Provider | Legacy Provider | Self-Paced Platform | Free Platform |
|---|---|---|---|---|---|
| Trainer Expertise & Credentials | |||||
| MCT-Certified Instructors | Partial | ✘ | ✘ | ✘ | |
| Live Instructor-Led Training | ✘ | ✘ | ✘ | ||
| 1-on-1 Private Mentorship | ✘ | ✘ | ✘ | ✘ | |
| EC-Council Authorization | |||||
| Official EC-Council ATC Status | ✘ | ✘ | ✘ | ||
| Official Courseware Access | ✘ | ✘ | ✘ | ||
| Hands-on Lab Hours | 40+ Hours | 40+ Hours | Variable | Variable | |
| Flexibility & Global Access | |||||
| Any-Day Start Flexibility | ✘ | ✘ | |||
| On-Site/Fly-Me Instructor | Partial | ✘ | ✘ | ✘ | |
| Global Delivery Reach | ✘ | ||||
| Results & Trust Signals | |||||
| Certification Pass Rate | 95% | N/A | N/A | N/A | N/A |
| Total Cost of Prep | $2,550 (All-in) | $3,000+ | $2,800 | $600 (3mo) | N/A |
| Verified Learner Reviews | 18,400+ · 4.9★ | Limited | Limited | 10,000+ · 4.2★ | N/A |
Data sourced from public pricing pages and review platforms. Accurate as of March 2026. Partial = available in select regions only.
Verified reviews from learners certified on Azure, AI, Security, and more.
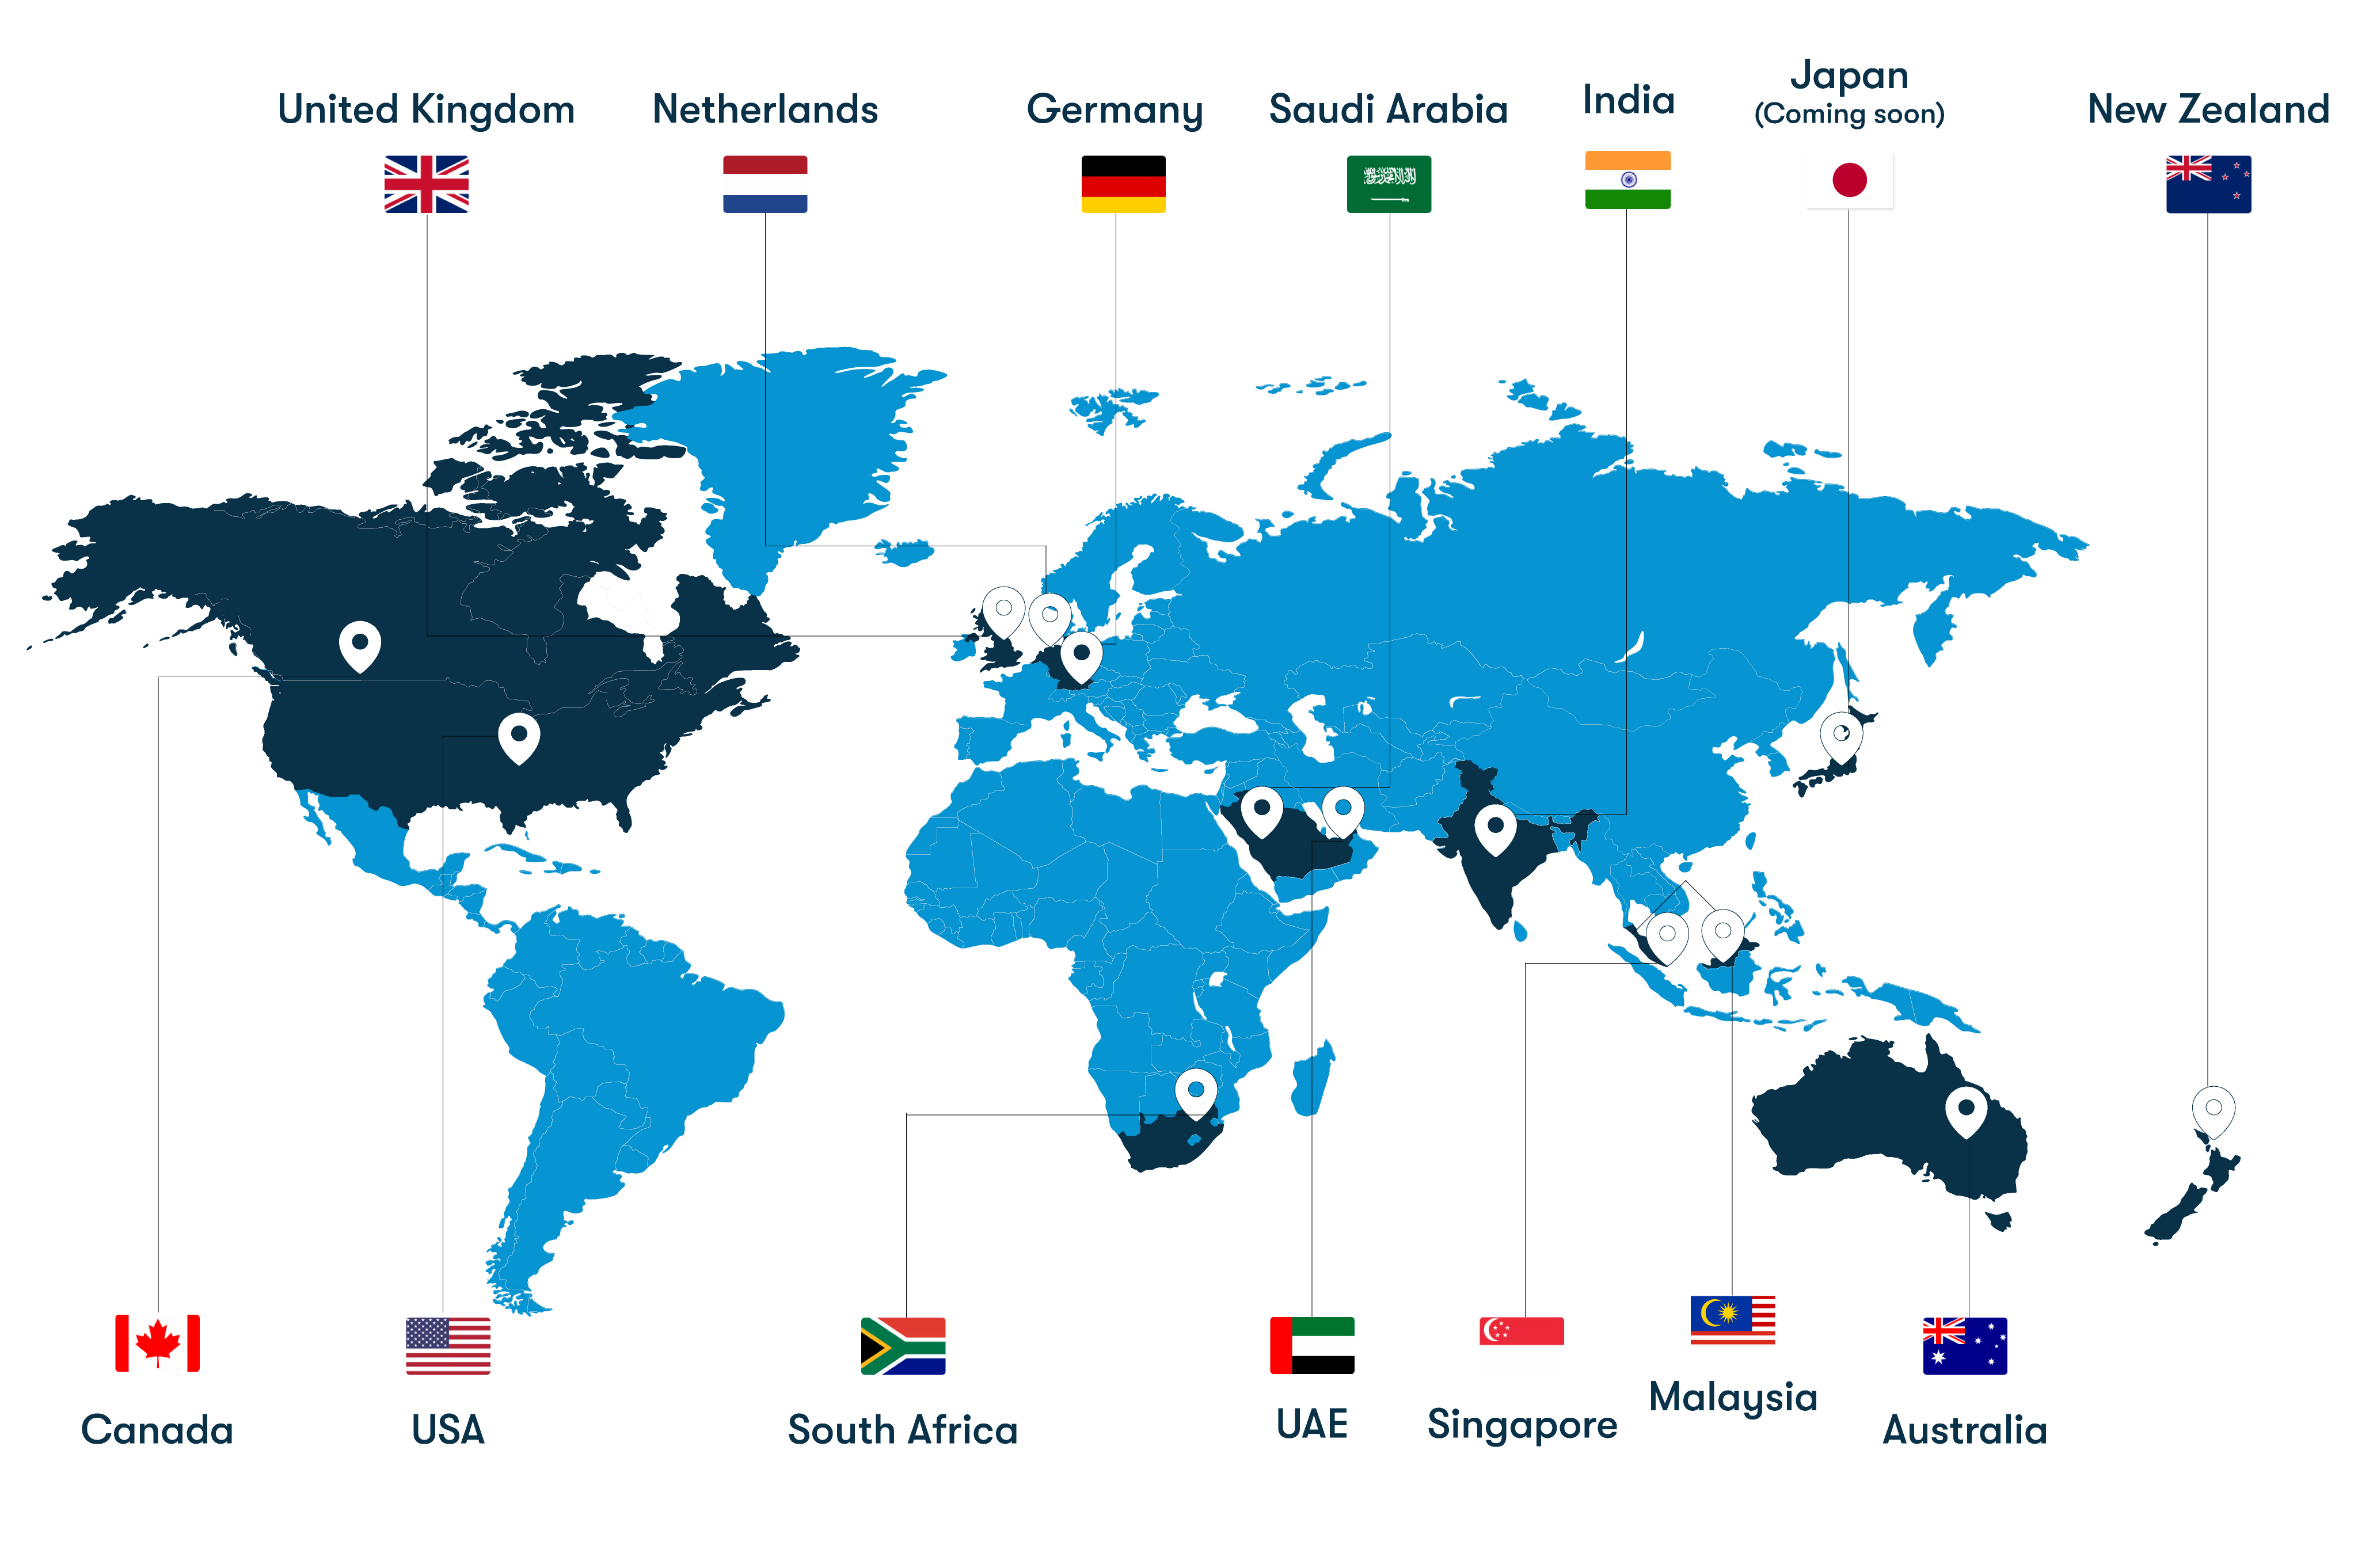
From our headquarters in India to training centers across UAE, Iraq, Saudi Arabia, UK, USA, Singapore, Australia, and more — Koenig delivers Microsoft certification training in 50+ countries.